Whitelisting: You Set The Rules For Security
We all know what blacklisting is when it comes to strings: removing specified "bad" characters. While this helps to secure user input, it isn't as secure as whitelisting. Whitelisting is the process of saying "Let me tell you what you can give me" whereas blacklisting says "If I find this, I'll remove it."
A customer recently asked that I create a whitelisting function that allowed letters, digits, whitespace characters, periods, commas, and dashes. Any other characters were to be replaced with spaces.
The PHP
function make_valid($input)
{
	return preg_replace('/[^A-Za-z0-9.,\(\)\s-]/',' ',$input);
}
The above function uses preg_match() and a small regular expression to remove the rubbish characters.
![Interview with a Pornhub Web Developer]()
Regardless of your stance on pornography, it would be impossible to deny the massive impact the adult website industry has had on pushing the web forward. From pushing the browser's video limits to pushing ads through WebSocket so ad blockers don't detect them, you have...
![An Interview with Eric Meyer]()
Your early CSS books were instrumental in pushing my love for front end technologies. What was it about CSS that you fell in love with and drove you to write about it?
At first blush, it was the simplicity of it as compared to the table-and-spacer...
![CSS Fixed Positioning]()
When you want to keep an element in the same spot in the viewport no matter where on the page the user is, CSS's fixed-positioning functionality is what you need.
The CSS
Above we set our element 2% from both the top and right hand side of the...
![Duplicate the jQuery Homepage Tooltips]()
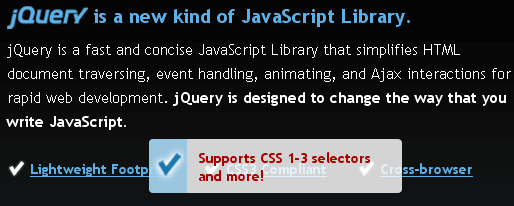
The jQuery homepage has a pretty suave tooltip-like effect as seen below:
The amount of jQuery required to duplicate this effect is next to nothing; in fact, there's more CSS than there is jQuery code! Let's explore how we can duplicate jQuery's tooltip effect.
The HTML
The overall...


Your way for whitelisting is quite nice. It’s like in Flash where you can specify exactly what characters are allowed by the user.
This method may work well as a common security filter that replaces get_magic_quotes_gpc(), strip_tags() and htmlentities().
Good work as usual!